Services
Government Solutions
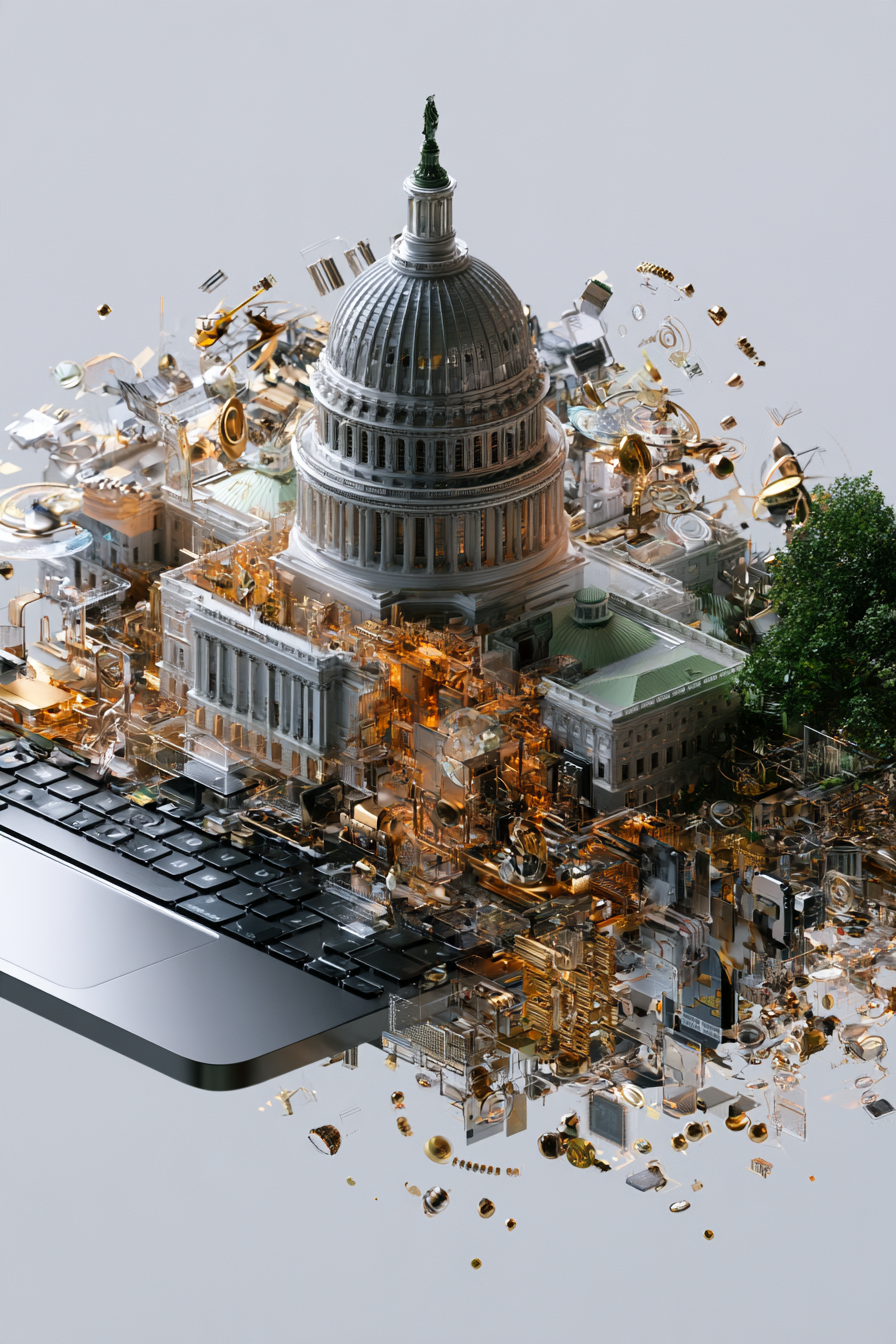
Government technology should support the mission with reliability, security and accountability
Government organizations operate in environments where technology decisions can affect public services, internal operations, regulatory obligations and the security of sensitive information.
The challenge is not simply to introduce newer systems. Government technology needs to perform reliably, integrate with existing infrastructure, support established processes and remain manageable within complex organizational and procurement environments.
Strong government technology solutions combine infrastructure, cybersecurity, software, cloud services, digital experience and long-term planning into a coordinated approach. The goal is to help agencies modernize without disrupting the services and responsibilities they already need to deliver every day.
Start with the mission, not the technology
Government technology projects should begin with an understanding of the mission the system is intended to support.
An agency may need to improve constituent services, strengthen internal operations, modernize aging infrastructure, improve security, automate administrative work or make information more accessible.
Define the operational outcome
A successful project should have a clear reason for existing.
The objective might be reducing processing time, improving system availability, consolidating infrastructure, strengthening access controls or replacing a manual workflow.
When the desired outcome is clear, technical decisions can be evaluated according to whether they support that objective.
Understand the users affected by the system
Government technology may serve employees, contractors, partner organizations or members of the public.
Each group can have different requirements around access, usability, security and availability.
Understanding those users early helps ensure that the resulting system works within the reality of how the agency operates.
Modernization should reduce risk rather than simply replace old technology
Government organizations often depend on systems that have been operating for many years.
Those systems may support critical workflows and contain important institutional knowledge even when the underlying technology has become difficult to maintain.
Assess legacy systems before replacing them
A legacy application may depend on databases, authentication services, file systems, reporting tools and external integrations that are not immediately visible.
Before modernization begins, those dependencies should be understood.
Replacing the visible interface without accounting for the systems behind it can create unexpected operational problems.
Modernization does not always require a complete rewrite
Some systems can be improved through incremental modernization.
New interfaces, APIs, authentication systems, cloud infrastructure or individual application components may be introduced while existing business logic remains in place.
This phased approach can reduce implementation risk while still moving the organization toward a more maintainable architecture.
Retire systems deliberately
Replacing a system does not automatically remove the old one from the environment.
Legacy infrastructure should have a defined retirement plan that addresses data retention, archival requirements, user access and dependent applications.
Without that process, organizations may continue maintaining duplicate systems long after migration is complete.
Cybersecurity should be built into every government technology initiative
Government organizations may manage sensitive operational information, personal data, administrative systems and infrastructure that requires strong protection.
Security should therefore be considered throughout architecture, implementation and operations rather than added after deployment.
Identity should be managed centrally
Employees, contractors and administrators should receive access based on their responsibilities.
Centralized identity management can make it easier to enforce authentication requirements, review permissions and remove access when it is no longer necessary.
Least privilege should guide access decisions
Users and systems should have only the permissions required to perform their functions.
Reducing unnecessary administrative privileges can limit the impact of compromised accounts and accidental changes.
Multi-factor authentication strengthens sensitive access
Administrative interfaces, remote access and critical applications should use strong authentication where appropriate.
Multi-factor authentication helps reduce the risk that compromised passwords alone will provide access to important systems.
Security architecture should reduce the attack surface
The more systems and services exposed unnecessarily, the more opportunities exist for unauthorized access.
Government environments should be designed with clear security boundaries.
Segment sensitive systems
Network segmentation can separate administrative systems, user devices, public services, guest networks and other technology environments.
This can limit unnecessary communication between systems and reduce the potential spread of malicious activity.
Minimize public exposure
Internal services should not be accessible from the public internet unless there is a clear operational reason.
Public-facing systems should be separated from internal infrastructure and protected with appropriate filtering, authentication and monitoring.
Secure administrative interfaces
Management portals, network devices, cloud consoles and administrative tools should receive stronger access controls than ordinary user applications.
Privileged access should be limited, monitored and reviewed periodically.
Continuous monitoring improves operational awareness
Government systems can generate large volumes of information about application activity, network health, authentication and infrastructure performance.
Monitoring allows teams to identify developing problems before they become larger incidents.
Monitor critical infrastructure
Servers, network devices, applications, cloud platforms and internet connections should be monitored according to their importance.
Availability, resource usage and system health can provide early warning of failures.
Centralize useful logs
Logs from multiple systems can help teams understand both operational problems and potential security incidents.
Centralized collection makes information easier to search and correlate.
Make alerts actionable
Monitoring systems should help teams identify meaningful problems rather than overwhelm them with low-value notifications.
Alerts should be prioritized according to operational impact and security risk.
Cloud adoption should be deliberate and governed
Cloud platforms can provide government organizations with scalable infrastructure, managed services and faster deployment capabilities.
They also introduce questions around data, identity, security, architecture and long-term cost.
Evaluate workloads individually
Not every system has the same requirements.
Some workloads may be strong candidates for public cloud infrastructure, while others may be better suited to private or hybrid environments.
Architecture decisions should reflect security, performance, availability, integration and operational requirements.
Establish governance before the environment grows
Cloud resources can be created quickly, which makes consistent standards especially important.
Organizations should define expectations around account structures, identity, network configuration, naming, tagging, security and cost ownership.
Use automation to improve consistency
Infrastructure as code and automated deployment can reduce configuration differences between environments.
Repeatable infrastructure also makes systems easier to rebuild, review and maintain.
Hybrid environments require clear integration
Government modernization rarely happens in one step.
On-premises systems, private infrastructure, SaaS platforms and cloud services may need to coexist for extended periods.
Design connectivity around real dependencies
Applications may need to communicate securely across offices, data centers and cloud platforms.
Network architecture should make those traffic paths clear and manageable.
Centralize identity where practical
Users should not need completely separate authentication models for every environment.
Consistent identity and access controls can make hybrid environments easier to secure and administer.
Maintain visibility across environments
Monitoring should not stop at the boundary between cloud and on-premises infrastructure.
Teams need enough visibility to understand how systems interact and where failures originate.
Government software should be built for long-term maintainability
Custom software may support permitting, case management, internal approvals, reporting, constituent services and many other government functions.
The application needs to remain maintainable long after the original implementation project is complete.
Use clear architecture
Application components should have defined responsibilities and predictable interfaces.
Separating business logic, data access, user interfaces and integrations can make future changes easier to manage.
Avoid unnecessary technical complexity
Sophisticated technology should be introduced when it solves a real requirement.
Overly complicated architectures can increase maintenance costs and make future support dependent on specialized expertise.
Document important decisions
Architecture, configuration, data structures and integration decisions should be documented so future teams can understand how the system works.
Documentation is particularly important when contracts, vendors or personnel may change over the life of the system.
APIs can help modernize disconnected government systems
Government organizations often depend on multiple specialized applications that need to exchange information.
APIs can provide structured connections between those systems.
Reduce duplicate data entry
When employees manually transfer the same information between systems, the process consumes time and creates opportunities for error.
Integrations can synchronize information automatically where business rules allow.
Create reusable services
Common capabilities such as identity verification, document generation, payment processing or notification services may be exposed through reusable interfaces.
This can reduce duplication across multiple applications.
Design integrations for failure
External systems may become unavailable or return incomplete information.
Applications should include appropriate validation, logging, retries and error handling so a temporary integration issue does not create a larger operational failure.
Data should be treated as a strategic government asset
Government organizations often maintain large amounts of information across operational systems, databases, spreadsheets and document repositories.
The value of that information depends on whether it is accurate, accessible and governed appropriately.
Establish authoritative data sources
Organizations should understand which systems are considered the trusted sources for important information.
Clear ownership reduces inconsistencies when the same data appears in multiple applications.
Improve data quality
Incomplete, duplicated or inconsistent data can undermine reporting and operational decision-making.
Validation, standardization and governance can improve reliability across systems.
Protect sensitive information
Sensitive data should be secured according to its classification and operational requirements.
Access controls, encryption, retention policies and monitoring should reflect the type of information being protected.
Digital government services should be designed around the public experience
Government websites and applications may be the primary way members of the public interact with an agency.
The experience should make it easy for users to understand information, complete transactions and access services.
Organize information around user needs
Members of the public should not need to understand internal agency structure to find what they need.
Navigation and page architecture should reflect common tasks and user expectations.
Make important actions obvious
Applications, forms, payments, appointments and service requests should be easy to locate.
Clear calls to action reduce confusion and can reduce the number of users who require assistance through other channels.
Use plain language where possible
Government processes can involve complex terminology.
Digital interfaces should explain requirements in language that users can understand without removing necessary legal or technical precision.
Accessibility should be part of digital delivery
Government digital services should be usable by people with different abilities and methods of interaction.
Accessibility is most effective when incorporated into design and development from the beginning.
Use semantic HTML
Headings, forms, navigation, tables, buttons and links should use appropriate markup so assistive technologies can interpret the interface correctly.
Support keyboard interaction
Users should be able to navigate and operate important functionality without relying entirely on a mouse.
Focus states should remain visible and interactions should follow a logical order.
Provide accessible forms
Form fields should have meaningful labels, clear instructions and understandable error messages.
Users should be able to determine what information is required and how to correct a problem.
Test accessibility continuously
Automated testing can identify many common issues, but it cannot evaluate every aspect of usability.
Accessibility review should include manual inspection and testing of important user journeys.
Performance and reliability directly affect public services
A slow or unavailable government system can prevent users from completing important tasks.
Performance should therefore be considered part of service delivery rather than only a technical metric.
Monitor application performance
Response time, error rates and resource consumption can help teams identify problems before they create widespread disruption.
Optimize high-volume workflows
Forms, search tools, public portals and other frequently used functions should be tested under realistic levels of demand.
Systems that perform well during normal periods should also be evaluated for expected peaks in usage.
Design for graceful failure
Not every dependency will always be available.
Applications should provide understandable error messages and preserve user progress where practical when external systems or services fail.
Business continuity should be built into critical systems
Government operations may need to continue during infrastructure failures, cyber incidents, severe weather or other disruptions.
Technology planning should account for how critical systems will recover.
Identify essential services
Not every application requires the same level of availability.
Agencies should determine which systems support essential operations and prioritize those systems in continuity planning.
Define recovery objectives
Recovery time and acceptable data loss should be established according to the importance of each system.
Those objectives help determine backup frequency, redundancy and recovery architecture.
Test recovery procedures
A recovery plan should be exercised before an emergency occurs.
Testing helps identify technical dependencies, outdated documentation and unclear responsibilities.
Backups should be protected and verified
Backups support both disaster recovery and cybersecurity.
They should be managed as part of normal operations rather than treated as an emergency-only system.
Protect backups from the production environment
If backup systems use the same credentials and access paths as production infrastructure, a security incident may affect both environments.
Critical data may require isolated, immutable or separately secured backup copies.
Test restoration
A backup is valuable only if the information can be restored successfully.
Periodic recovery testing verifies that data is usable and procedures are realistic.
Network infrastructure should support both security and availability
Government systems depend on networks connecting offices, data centers, cloud environments and remote users.
Network design should provide reliable connectivity while maintaining clear security boundaries.
Use segmentation strategically
Administrative systems, general users, public services, guest traffic and specialized equipment may require different network zones.
Segmentation can improve both security and troubleshooting.
Build redundancy where operations require it
Critical locations may need multiple internet connections, redundant network equipment or alternate communication paths.
Redundancy should reflect the operational consequences of an outage.
Maintain visibility into network health
Monitoring bandwidth, latency, device availability and connectivity can help teams identify developing problems before users experience a complete interruption.
Physical infrastructure remains an important part of government technology
Government facilities may rely on extensive cabling, wireless infrastructure, network closets, fiber connections and audiovisual systems.
Physical infrastructure should be designed with the same attention to documentation and lifecycle management as software and cloud environments.
Structured cabling should support long-term use
Copper and fiber infrastructure should reflect bandwidth requirements, building design and expected future growth.
Clear labeling and documentation can significantly reduce maintenance time.
Wireless networks should be engineered for capacity
Wireless coverage alone does not guarantee a good experience.
User density, interference, building materials and device counts should all be considered when access points are placed.
Equipment environments should be maintained
Network rooms and equipment racks should have appropriate power, cooling, physical security and organization.
Infrastructure becomes harder to support when the physical environment is allowed to deteriorate.
Technology procurement should account for the full lifecycle
The cost of technology is not limited to the initial purchase.
Implementation, licensing, maintenance, support, training and eventual replacement all contribute to the total cost of ownership.
Evaluate long-term supportability
A system should be maintainable by the organization or its technology partners throughout its expected lifecycle.
Highly specialized technology may create long-term dependency if appropriate expertise is difficult to obtain.
Consider integration before purchase
A new platform may provide strong functionality while creating significant complexity if it cannot exchange information with existing systems.
Integration requirements should be evaluated before major technology decisions are finalized.
Plan for exit and migration
Organizations should understand how data can be exported and how the system could eventually be replaced if requirements change.
That knowledge can reduce unnecessary vendor lock-in.
Vendor management should include clear responsibilities
Government technology environments may involve multiple software vendors, cloud providers, contractors and managed service partners.
Clear responsibilities help prevent important tasks from falling between organizations.
Define ownership for operational tasks
Teams should understand who manages updates, security, backups, monitoring, incident response and user support.
Shared responsibility should still result in clearly assigned ownership.
Document escalation procedures
When a critical system fails, staff should know which vendor or team needs to be contacted and how the issue should be escalated.
Those processes should be documented before an emergency occurs.
Review vendor performance
Service quality should be evaluated over time according to operational needs rather than only during contract renewal.
Recurring problems may indicate that responsibilities, architecture or service expectations need to change.
Documentation creates continuity across teams and contracts
Government environments can experience changes in staff, leadership and technology providers over the life of a system.
Documentation reduces dependence on institutional memory.
Document infrastructure architecture
Network diagrams, system dependencies, cloud environments and major integrations should be understandable to future administrators.
Document operational procedures
Backup, deployment, user administration, recovery and troubleshooting procedures should be recorded where appropriate.
Keep documentation current
Outdated documentation can create confusion during incidents or transitions.
Updating documentation should be part of normal system changes.
Change management reduces unnecessary disruption
Government systems may support large numbers of users or critical public functions.
Changes should be introduced in a controlled way.
Test before production deployment
Updates should be evaluated in development or staging environments where practical before they are introduced to production systems.
Define rollback procedures
Teams should understand how to restore a previous stable configuration when a change creates unexpected problems.
Communicate changes to affected users
Technical changes can create confusion even when the underlying implementation is successful.
Users should receive appropriate guidance when workflows, interfaces or access procedures change.
Automation can reduce repetitive administrative work
Government organizations may rely on manual processes involving forms, approvals, data transfer and recurring reports.
Automation can reduce the amount of time employees spend on routine work while improving consistency.
Automate repeatable workflows
Document routing, notifications, data synchronization and routine status updates may be candidates for automation.
The strongest opportunities are usually processes that occur frequently and follow predictable rules.
Preserve human review where judgment matters
Automation should not remove oversight from decisions that require professional judgment, policy interpretation or significant discretion.
Technology can prepare information and route work while leaving final decisions with the appropriate personnel.
Artificial intelligence should be introduced around clearly defined use cases
AI can support document analysis, information retrieval, workflow automation, software development and data analysis.
Government adoption should begin with specific operational problems rather than technology experimentation without a clear objective.
Understand the data involved
Before using an AI service, organizations should understand what information will be submitted, how it will be processed and whether the use case involves sensitive data.
Keep appropriate oversight
AI-generated outputs may be incomplete or inaccurate.
High-impact decisions should include validation and human review appropriate to the consequences of the decision.
Measure whether AI is creating value
An AI project should be evaluated according to measurable outcomes such as reduced processing time, improved information retrieval or increased productivity.
The presence of AI alone is not evidence that a system has improved.
Technology planning should account for workforce capabilities
Modern systems still depend on people who understand how to operate and maintain them.
Government technology strategies should consider the skills required throughout the system lifecycle.
Identify capability gaps
Organizations should understand which capabilities exist internally and which may require specialized outside expertise.
Networking, cloud architecture, cybersecurity and software engineering may require different skill sets.
Support knowledge transfer
External specialists should not become the only source of knowledge about critical systems.
Documentation, training and collaboration can help internal personnel understand the environments they are responsible for.
Design systems that future teams can maintain
Technology should not be so specialized that ordinary maintenance requires recreating the original project team.
Maintainability should be considered an architectural requirement.
Technology roadmaps help agencies modernize in manageable phases
Government environments often contain more modernization opportunities than can be addressed at once.
A technology roadmap can prioritize initiatives according to risk, mission value, cost and dependency.
Address foundational issues first
Identity, networking, security and data architecture may need improvement before more visible digital initiatives can succeed.
Fixing those foundations can make future projects easier to implement.
Sequence projects deliberately
Applications and infrastructure frequently depend on one another.
Migration plans should reflect those dependencies rather than treating each technology project as an isolated effort.
Deliver incremental value
Large modernization programs do not need to wait years before producing benefits.
Phased delivery can improve individual workflows and systems while the broader architecture continues to evolve.
Performance should be measured against operational outcomes
Government technology should be evaluated according to how well it supports the work it was designed to enable.
Technical metrics are useful, but they should connect to real service outcomes.
Measure reliability
Availability, incident frequency and recovery time can indicate whether critical systems are becoming more dependable.
Measure process improvements
If a system was intended to reduce manual work or accelerate a process, completion time and error rates may provide meaningful measures of success.
Measure user experience
Support volume, user feedback and task completion can help identify whether employees or members of the public are actually benefiting from a technology change.
Government technology requires long-term ownership
A successful implementation is not the end of a system’s lifecycle.
Software needs updates. Infrastructure ages. Security requirements evolve. User needs change.
Define who owns the system after launch
Responsibility for monitoring, maintenance, security, support and future improvements should be clear.
Plan for lifecycle replacement
Hardware and software should not remain in production indefinitely simply because they continue to function.
Organizations should understand vendor support timelines and plan upgrades before systems become unsupported.
Continue improving the environment
Technology strategy should be reviewed periodically as organizational priorities, risks and capabilities change.
Modernization is most effective when it becomes an ongoing discipline rather than a series of emergency replacement projects.
The strongest government technology becomes a dependable part of the mission
Government organizations need technology that can operate within complex environments without creating unnecessary complexity of its own.
That requires more than selecting products or deploying infrastructure. It requires understanding the mission, designing secure architecture, managing data, integrating systems, supporting users and planning for the full lifecycle of the technology.
When those elements work together, modernization becomes more manageable and technology becomes more resilient.
The result is an environment that can support employees, improve digital services and adapt as requirements evolve.
That is the purpose of effective government technology: not technology for its own sake, but dependable systems that help public organizations carry out their responsibilities with greater security, efficiency and confidence.